Samurai [Pen-testing Distro]

The Samurai Web Testing Framework is a LiveCD focused on web application testing. We have collected the top testing tools and pre-installed them to build the perfect environment for testing applications.

[Download]

ModSecurity v2.7

ModSecurity is an embeddable web application firewall, which means it can be deployed as part of your existing web server infrastructure (Apache, IIS7 and Nginx).

This deployment method has certain advantages:

  1. No changes to existing network. It only takes a few minutes to add ModSecurity to your existing web servers. And because it was designed to be completely passive by default, you are free to deploy it incrementally and only use the features you need. It is equally easy to remove or deactivate it should decide you don't want it any more.
  2. No single point of failure. Unlike with network-based deployments, you will not be introducing a new point of failure to your system.
  3. Implicit load balancing and scaling. Because it works embedded in web servers, ModSecurity will automatically take advantage of the additional load balancing and scalability features. You will not need to think of load balancing and scaling unless your existing system needs them.
  4. Minimal overhead. Because it works from inside the web server process there is no overhead for network communication and minimal overhead in parsing and data exchange.
  5. No problem with encrypted or compressed content. Many IDS systems have difficulties analysing SSL traffic. This is not a problem for ModSecurity because it is positioned to work when the traffic is decrypted and decompressed.
ModSecurity is known to work well on a wide range of operating systems. Our customers are successfully running it on Linux, Windows, Solaris, FreeBSD, OpenBSD, NetBSD, AIX, Mac OS X, and HP-UX.

Joomla Vulnerability Scanner

Description


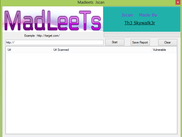
its a Joomla Vulnerability Scanner made by .net  You need dotnet framework 4.5 for use it. made by skywalk3r for Madleets.

PySQLi - Python framework to exploit complex SQL injection vulnerabilities

PySQLi is a python framework designed to exploit complex SQL injection vulnerabilities. It provides dedicated bricks that can be used to build advanced exploits or easily extended/improved to fit the case.

PySQLi is thought to be easily modified and extended through derivated classes and to be able to inject into various ways such as command line, custom network protocols and even in anti-CSRF HTTP forms.

PySQLi is still in an early stage of development, whereas it has been developed since more than three years. Many features lack but the actual version but this will be improved in the next months/years.

Download PySQLi

Faraday [Penetration Test IDE]

Faraday introduces a new concept (IPE) Integrated Penetration-Test Environment a multiuser Penetration test IDE. Designed for distribution, indexation and analysis of the generated data during the process of a security audit.
The main purpose of Faraday is to re-use the available tools in the community to take advantage of them in a multiuser way.

Design for simplicity, users should feel no difference between their own terminal application and the one included in Faraday. Developed with a specialized set of functionalities that help users improve their own work. Do you remember yourself programming without an IDE? Well, Faraday does the same an IDE does for you when programming, but from the perspective of a penetration test.

[Download]

IP-DiggER v 3.0 - The WeB Xploit3r by Team FreakCoderz

Features
PHP Server Based

SQLI Websites
XSS Websites
LFI Websites
RFI Websites
Admin Panels
Upload Vulnerability

ASP Server Based

ASP SQLI Websites
ASP XSS Websites
ASP Admin Panels
ASP Upload Vulnerability

Website Related Tools

Wordpress Website Finder
Joomla Website Finder
Sub Domain Scanner
Web Terminator ( DDos Attack )
IP Resolver
NS Lookup
Joomla Website Vulnerability Scanner

[Download]

LFI Server Scanner

BTS Pen-testing Lab


BTS PenTesting Lab is a vulnerable web application that helps you in learning basic to advanced vulnerability types. The App is still in Beta version(v0.2).
Currently, the app allows you to learn the following vulnerability types:
SQL Injection
XSS
CSRF
Clickjacking
SSRF
File Inclusion
Command Execution
I am trying to bring some advanced vulnerability types and advanced techniques. Hopefully, you can see in next update :)
The app is developed by Sabari Selvan, a security researcher at Cyber Security Privacy Foundation(cysecurity.org)

How to run BTS PenTesting Lab?
1. Install XAMPP or WAMPP in your machine
2. Extract the bts_lab zip file into the htdocs folder.
3.  Open the "http://localhost/bts_lab/setup.php" url in your browser.
4. Click the Setup.
Now you can use http://localhost/bts_lab in Browser

[Download]

Exploit Pack [The most advanced and easy to use tool for pentesters]

Exploit Pack is an open source GPLv3 licensed bundle of scripts ( known as exploits ) with an easy to use GUI and a SID IDE. It’s built on JAVA and Python, which means it’s easy to customize and works very nicely on any device. Like every software that has an open source license you can patch, extend or add your own ideas to it. Just checkout the code and go for it. This tool was made thinking on the end-user, it's not going to replace any other security tool on the market, but it's for sure a must-have for every security enthusiast, researcher or paranoid user.

It's easy to use

Hello script kiddie. Don't you worry, you can always use this tool without reading any kind of documentation. But shame on you.

Multi OS support

It was developed thinking on multi platform support by default for x86 but it will run on Windows, Linux, FreeBSD and Mac OSX.

IDE for Exploit Dev's

A must-have for effective exploit development, extend or add more features and include your own exploit codes. 

Python Programming eBook Collection [pdf]

Copyright © 2013 Hacking Tools and Tech eBooks Collection and Blogger Templates - Anime OST.