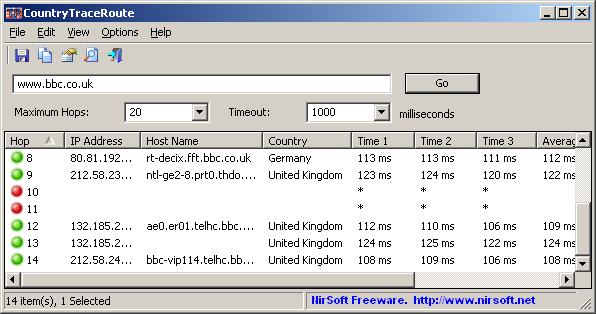
CountryTraceRoute v1.20

CountryTraceRoute is a Traceroute utility, similar to the tracert tool of Windows, but with graphical user interface, and it's also much faster than tracert of Windows. CountryTraceRoute also displays the country of the owner of every IP address found in the Traceroute.
After the Traceroute is completed, you can select all items (Ctrl+A) and then save them into csv/tab-delimited/html/xml file with 'Save Selected Items' option (Ctrl+S) or copy them to the clipboard (Ctrl+C) and then paste the result into Excel or other spreadsheet application.

[Download]   

Shell OS Released


Description

Build by Rajib Acharyya(Spid3r64)


ANONIMITY

Metasploit Armitage Cobalt Strike & veil
WIRELESS SECURITY
SNIFFERS
PYTHON,PERL & RUBY
FORENSICS
BRUTE FORCE
&
DDOS
ANDROID TOOLS

Based on : Ubuntu 12.04 LTS(32bit) (Custom Backbox)
user:root
pass:india

Kernel version =>3.8.0-29 generic
Desktop environment's => xfce,conky,Docky
Version 1.0(full)


Extra Softwares inbuilt => Skype,Virtualbox,Filezila,Chromium Browser,XDM(Xtreme Download Manager) ,Gimp,Python...many more.

BurpSuite Pro 1.6 Cracked [BETA]

Burp Suite is an integrated platform for performing security testing of web applications. Its various tools work seamlessly together to support the entire testing process, from initial mapping and analysis of an application's attack surface, through to finding and exploiting security vulnerabilities.
Burp gives you full control, letting you combine advanced manual techniques with state-of-the-art automation, to make your work faster, more effective, and more fun.

[Download] [Mirror]

Password: Download

Advanced SQLi [PDF]

Advanced SQLi In SQL Server Applications
Fle Type: pdf
Size: 291KB
<Download>

WirelessKeyView [Recover lost wireless network key]

 WirelessKeyView recovers all wireless network security keys/passwords (WEP/WPA) stored in your computer by the 'Wireless Zero Configuration' service of Windows XP or by the 'WLAN AutoConfig' service of Windows Vista, Windows 7, Windows 8, and Windows Server 2008. It allows you to easily save all keys to text/html/xml file, or copy a single key to the clipboard. You can also export your wireless keys into a file and import these keys into another computer.


[WAF-FLE v0.6.3] Web application firewall: fast log and event console

 WAF-FLE is a OpenSource Console for ModSecurity, it allow the modsec admin to view and search events sent by mlogc (modsecurity event log handler).


Features:
  • Central event console
  • Support Modsecurity in “traditional” and “Anomaly Scoring”
  • Able to receive events sent from mlogc (in real time or in batch using mlogc-batch-load.pl)
  • No sensor number limit
  • Dashboard with recent events information
  • Drill down of events with filter
  • Every (almost) data is “clickable” to drill down the filter
  • Inverted filter (to filter for “all but this item”)
  • Filter for network (in CIDR format, x.x.x.x/22)
  • Raw event download
  • Use Mysql as database
  • Open Source released under GPL v2

Charles [Web Debugging Proxy Application]

Charles is a web proxy (HTTP Proxy / HTTP Monitor) that runs on your own computer. Your web browser (or any other Internet application) is then configured to access the Internet through Charles, and Charles is then able to record and display for you all of the data that is sent and received.
In Web and Internet development you are unable to see what is being sent and received between your web browser / client and the server. Without this visibility it is difficult and time-consuming to determine exactly where the fault is. Charles makes it easy to see what is happening, so you can quickly diagnose and fix problems.


Charles makes debugging quick, reliable and advanced; saving you time and frustration!

Key Features

  • SSL Proxying – view SSL requests and responses in plain text
  • Bandwidth Throttling to simulate slower Internet connections including latency
  • AJAX debugging – view XML and JSON requests and responses as a tree or as text
  • AMF – view the contents of Flash Remoting / Flex Remoting messages as a tree
  • Repeat requests to test back-end changes
  • Edit requests to test different inputs
  • Breakpoints to intercept and edit requests or responses
  • Validate recorded HTML, CSS and RSS/atom responses using the W3C validator

SecLists [Collection of multiple types of lists used during security assessments]

SecLists is a collection of multiple types of lists used during security assessments. List types include usernames, passwords, URLs, sensitive data grep strings, fuzzing payloads, and many more.
The goal is to enable a security tester to pull this repo onto a new testing box and have access to every type of list that may be needed.


If you have any ideas for things we should include, please send them to daniel.miessler@owasp.org or jason.haddix@owasp.org. Also note that any lists that have been meticulously assembled by someone else will only be used with permission of the creator.
This project is maintained by Daniel Miessler and Jason Haddix. 
Credits:
- Ron Bowes of SkullSecurity for collaborating and including all his lists here
- Clarkson University for their research that led to the Clarkson list
- All the authors listed in the XSS with context doc, which was found on pastebin and added to by us
- Ferruh Mavitina for the begginings of the LFI Fuzz list
- Adam Muntner and  for the FuzzDB content, including all authors from the FuzzDB project
- Kevin Johnson for laudnaum shells
- RSnake for fierce hostname list 


[Suricata 1.4.2] Next Generation Intrusion Detection and Prevention Engine


The Suricata Engine is an Open Source Next Generation Intrusion Detection and Prevention Engine. This engine is not intended to just replace or emulate the existing tools in the industry, but will bring new ideas and technologies to the field.
OISF is part of and funded by the Department of Homeland Security's Directorate for Science and Technology HOST program (Homeland Open Security Technology), by the the Navy's Space and Naval Warfare Systems Command (SPAWAR), as well as through the very generous support of the members of the OISF Consortium. More information about the Consortium is available, as well as a list of our current Consortium Members


 The Suricata Engine and the HTP Library are available to use under the GPLv2
The HTP Library is an HTTP normalizer and parser written by Ivan Ristic of Mod Security fame for the OISF. This integrates and provides very advanced processing of HTTP streams for Suricata. The HTP library is required by the engine, but may also be used independently in a range of applications and tools. 

Improvements

  • No longer force "nocase" to be used on http_host
  • Invalidate rule if uppercase content is used for http_host w/o nocase
  • Warn user if bpf is used in af-packet IPS mode
  • Better test for available libjansson version

Fixes


  • Fixed accuracy issues with relative pcre matching (#784)
  • Improved accuracy of file_data keyword (#788)
  • Invalidate negative depth (#770)
  • Fix http host parsing for IPv6 addresses (#761)
  • Fix fast.log formatting issues (#773)
  • Fixed deadlock in flowvar set code for http buffers (#801)
  • Various signature ordering improvements
  • Minor stream engine fix

Hardanger [Web Application Penetration Testing Platform]

Hardanger is an Open Source web application penetration testing tool led by security researchers from SecurityWire. The project aims to bridge the gap between current open source web application testing tools commonly used in a Linux environment and bring the same level of tools to native Windows based platforms. Hardanger aims to deliver a user friendly experience for semi-automated web application penetration testing by building tools on top of the excellent Fiddler2 web debugger.


The project deliverable is a Fiddler2 (http://www.fiddler2.com) add-on dll written in C# that is easily installed using a .msi installer and a standalone application is also be available for users that do not want the integrated Fiddler2 experience. Hardanger has been architected so it can be easily expanded to add other functionality. The first version only includes a simple HTTP(S) GET and POST parameter fuzzer but will has built a foundation where it is trivial to plug in additional fuzzers and detection engines as well as other features. Once server fuzzing is perfected and state of the art, this project will continue to add new features such as a web browser fuzzer, brute force tool, manual tampering, crawler, passive vulnerability detection, recon tools, etc.


Current Features
  • Native Windows feel via Windows Presentation Foundation
  • Can run as a Fiddler2 add-on or standalone
  • ClickOnce installer with automatic updates (standalone version)
  • Context tab allowing inspection of full HTTP requests
  • Server fuzzer tab to configure and launch the server fuzzer
  • Basic random fuzzer generates random strings of UTF8 characters of random lengths
  • Non HTTP 200 detection engine
  • Results window keeping track of successful detections
  • Ability to review requests/responses in the results details window


Copyright © 2013 Hacking Tools and Tech eBooks Collection and Blogger Templates - Anime OST.